Letting Data Speak, AI Act!
Case Study
Data EngineeringAutomated High-Performance VDI for Semiconductor Workforce Development
Overview
A US semiconductor workforce development organization needed a secure, scalable cloud desktop platform to provide engineers with access to cost-prohibitive EDA tools but lacked the automated infrastructure to control costs and enforce enterprise identity policies. JashDS delivered a fully automated EC2 lifecycle platform integrating Microsoft Entra ID with Amazon Cognito and NICE DCV, reducing idle compute costs by up to 60% and enforcing 100% MFA compliance across a geo-restricted environment.
About the Client
A US-based semiconductor industry dedicated to democratizing access to specialized electronic design automation (EDA) software. The client partners with fabrication facilities and software vendors to support workforce development and the domestic supply chain by making high-cost design tools accessible to engineers and students.
The Challenge
The organization faced significant barriers in delivering secure, scalable, and cost-efficient high-performance cloud desktops to a growing distributed user base:
- High Compute Requirements: EDA and semiconductor design workloads required dedicated EC2-based desktop environments, creating risks of cost overruns and resource sprawl.
- Lack of Automation: No automated provisioning during user onboarding or lifecycle management (e.g., hibernating idle instances), resulting in unnecessary compute spend.
- Identity & Security Gaps: Absence of seamless federation with Microsoft Entra ID (Azure AD) limited enforcement of SSO and MFA for enterprise-grade authentication.
- Geo-Restriction Requirements: Access needed to be limited to US-based users with geo-location controls, which were not natively supported.
- Decommissioning Risks: Missing automated termination workflows (including EC2 snapshots and monitoring cleanup) increased the risk of data loss and orphaned resources.
Key Results
- Reduced cloud compute costs by 45-60% by implementing automated hibernation logic based on composite CPU and network inactivity thresholds.
- Decreased user provisioning time by 90%, enabling immediate access to personalized Linux desktop environments at first authentication.
- Strengthened identity security with 100% MFA and SSO enforcement via Microsoft Entra ID federated through Amazon Cognito, eliminating credential sprawl.
- Achieved full geo-compliance by enforcing VPN-based, US-only access with centralized monitoring and audit controls.
- Enhanced operational resilience through end-to-end automated EC2 lifecycle management, including provisioning, backup, hibernation, and secure termination workflows.
Our Solution
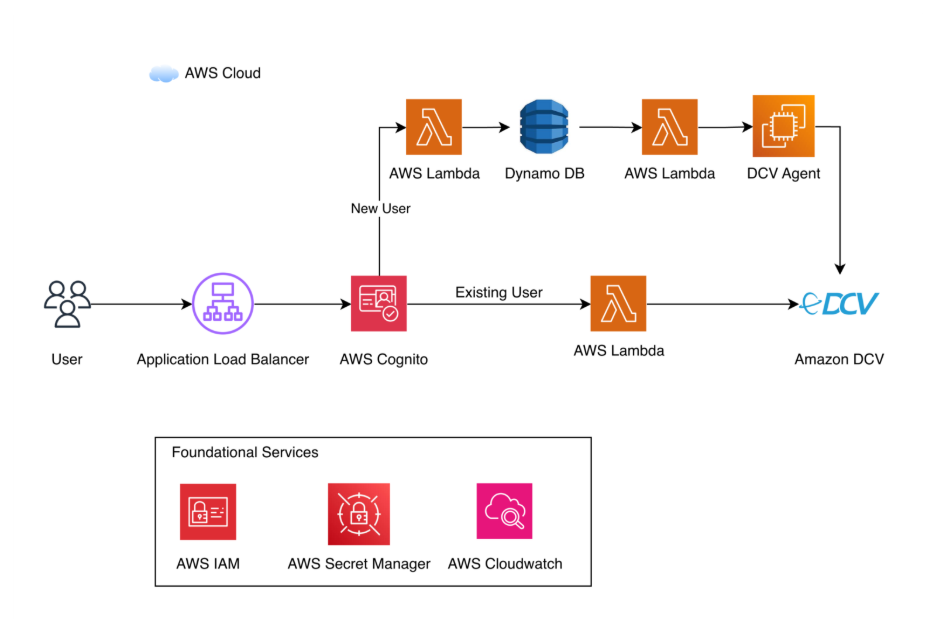
JashDS delivered a fully automated, event-driven cloud desktop platform built on AWS, enabling scalable per-user EC2 environments accessed through the NICE DCV Access Console. integrating enterprise identity federation, instance lifecycle orchestration, and intelligent resource optimization
- Identity Federation & Security: Integrated Microsoft Entra ID (Azure AD) with Amazon Cognito to handle authentication and session management. This enabled Enterprise SSO while enforcing Multi-Factor Authentication (MFA) and ensuring that only authorized US-based users could access the platform.
- Automated Lifecycle Management: Developed a robust orchestration layer using AWS Lambda and DynamoDB Streams. When a user authenticates for the first time, the system automatically provision a dedicated, hardened EC2 instance. Subsequent logins (hibernated state) trigger a "wake-up" sequence, transitioning instances from a stopped state to active availability in seconds.
- Cost-Optimized Hibernation: Implemented intelligent resource monitoring using Amazon CloudWatch. Custom alarms track CPU utilization (below 2.2%) and Network throughput (below 10MB). When thresholds indicate inactivity, a composite alarm triggers a Lambda function to hibernate the instance, preserving the memory state and user data while halting compute charges.
- High-Performance Visualization: Deployed the NICE DCV Connection Gateway to tunnel traffic securely. This allowed users to access applications via a web browser without direct exposure to the underlying agent IP addresses.
- Workflow Termination: A dedicated Lambda function was deployed to accept lists of user IDs, automatically creating EBS snapshots for backup, terminating associated EC2 instances, and cleaning up related CloudWatch alarms to ensure no orphaned resources remained.
- Security Hardening: EC2 instances were launched from pre-hardened AMIs. Access was restricted through VPN connectivity and geo-location-based security controls, limiting platform access to US-based users only. Credentials were fully managed through Cognito with MFA enforcement delegated to Entra ID policies.
Technologies Used
Related Case Studies
← Back to All Case Studies
Data Engineering
Azure to AWS SaaS Platform Migration
An EdTech SaaS company migrated its entire Azure-hosted student risk monitoring platform to AWS in 9 weeks — lifting and shifting 17 VMs, 12 PostgreSQL databases, and multiple application services with zero disruption to school district operations. The solution leveraged Terraform, AWS Control Tower, and a fully automated CI/CD pipeline to deliver a scalable, cost-optimized cloud foundation built for rapid expansion.
Read More
Data Engineering
Real-Time AI Chatbot Platform’s Lambda to ECS Migration
An AI chatbot startup faced critical Lambda performance issues including 100% memory utilization causing crashes, 7-8 second cold starts,Scalability issues where in multiple concurrent users using this application concurrently faced issues to use the application which includes laginess taking too much time to get the response, application crashing and completely non-functional WebSocket group chat due to protocol incompatibility between Socket.IO frontend and API Gateway WebSocket backend. Through a 4-week POC engagement, we successfully containerized Lambda functions to ECS Fargate, conducted systematic JMeter load testing up to 1,000 concurrent users, and delivered complete Terraform Infrastructure-as-Code, achieving 94% response time reduction (to sub-1-second), 100% cold start elimination, 0% error rate, and validated linear horizontal scalability while providing all technical documentation and architecture recommendations for production migration decision-making.
Read More
Data Engineering
Workload migration from on-prem to AWS - MAP Assessment
An ed-tech company needed to move 340 TB of unstructured data and a stateful PHP platform from an aging co-location to AWS despite a 15 Mbps link that made online transfer impractical. MAP Assessment defined a Hybrid Snowball Edge + DataSync “Seed and Sync” approach that cut the data migration from an infeasible 1+ year to ~5–6 weeks, enabled phased S3 tiering for ~62% lower ongoing storage costs, and used AWS DMS CDC to achieve near-zero downtime database migration with near-real-time RPO.
Read MoreHave a similar challenge?
Connect with us